SAP Security
Operations Reinvented
From Reactive Security to Continuous Controls
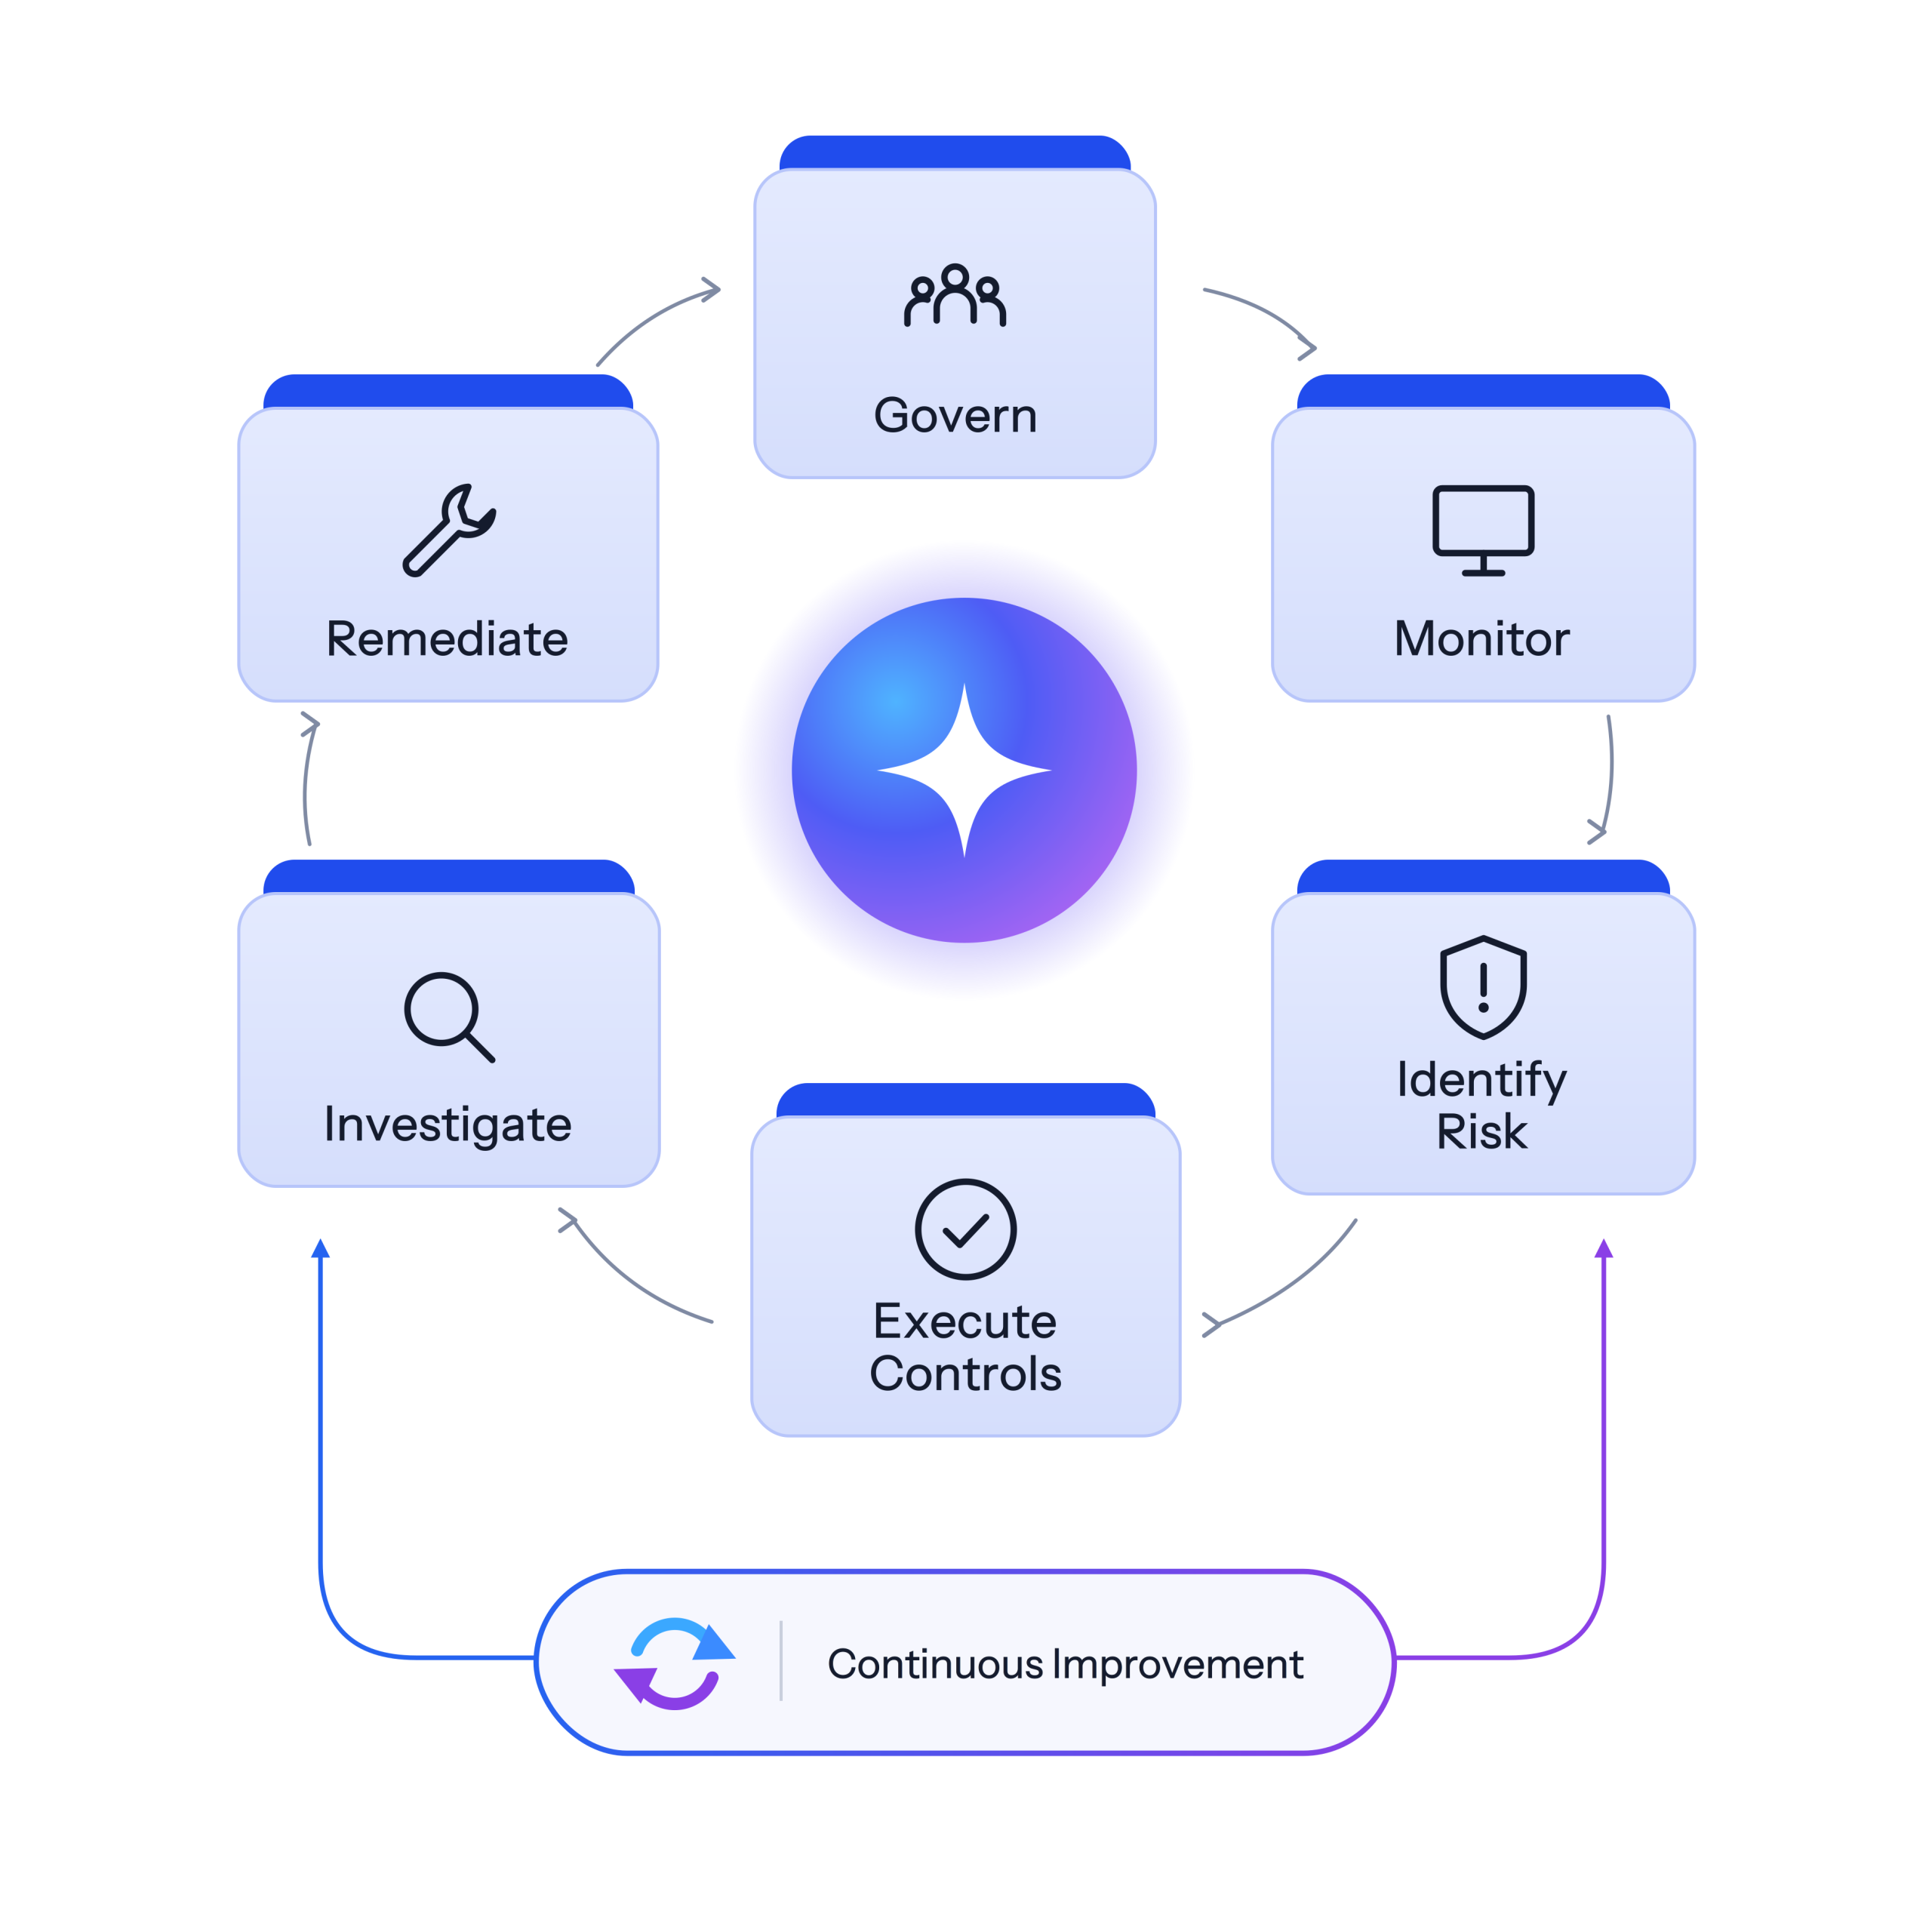
SAP Security must not start when an audit begins. ToggleNow SecOps embeds continuous governance, risk monitoring, controls validation, and automated response into the day-to-day operations.
What is ToggleNow SecOps for SAP?
ToggleNow SecOps for SAP is an AI-embedded Access Governance Platform that unites People + Process + Platform to continuously secure, govern and transform your SAP landscape.
Many organizations still see SAP Security as an add-on to SAP BASIS or incident management focusing on password resets, user provisioning, role assignments, access requests and day-to-day support.
But, handling security incidents is not the same as securing SAP.
ToggleNow SecOps changes that mindset. It automates repetitive L1/L2/L3 activities, allowing security teams to spend less time on tickets and more time on identifying risks, strengthening controls and improving the security posture of SAP.
It combines Risk Management, Access Governance, Controls, Security Monitoring, Audit & Compliance, License Governance, Automation and AI under one operational framework.
ToggleNow SecOps turns SAP Security from reactive incident management into a continuous security operation.
Why traditional SAP security
is no longer sufficient
Why traditional SAP security is no longer sufficient
SAP landscapes are now hybrid, cloud-first and constantly changing. New users, roles, integrations, technical accounts and business processes are created every day.
A traditional, periodic approach cannot keep up with this pace. Enterprises need a continuous security model that monitors, detects and responds to risks in real time.
Periodic
Point-in-time audits and reviews
Continuous
Real-time monitoring and ongoing risk visibility
What users ask
Access based on user requests
What users need
Access based on business context, risk and least privilege
People
Manual effort and siloed ownership
People + process + platform, with AI
Automation, AI-driven insights and unified governance
A side practice
Treated as an audit or compliance activity
A core practice
Built into day-to-day operations and business transformation
ToggleNow brings it's EEAT methodology in every engagement. Thus, we don't have to re-invent the wheel.
Traditional Security Model
Traditional security focuses on incidents, audits and periodic reviews. ToggleNow SecOps focuses on continuously securing the SAP environment.
AI Embedded
ToggleNow SecOps combines people, process and platform with AI embedded across SAP security operations for governance and protection
Security Team Impact
Security teams can reduce effort and focus on monitoring, detection, response and risk reduction across SAP security operations.
Business Outcome
Your SAP environment stays continuously security-ready, making security an operational practice rather than an audit-driven compliance exercise.
SAP Security must not start
when an audit begins.
SAP Security must not start when an audit begins.
Governance
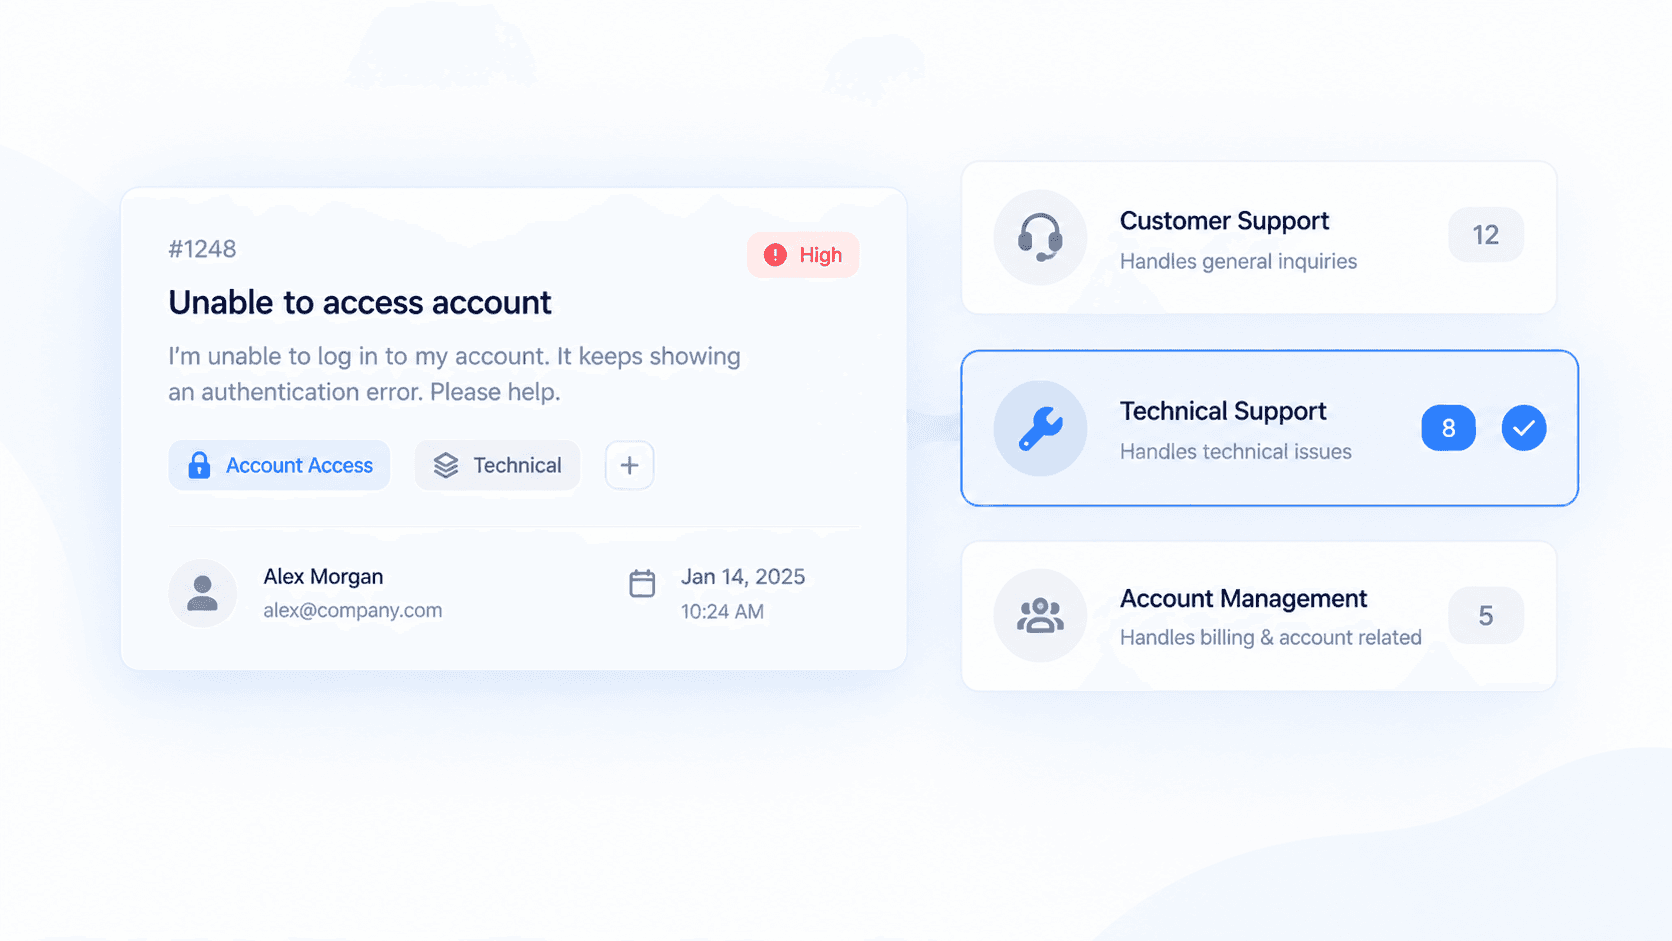
Support Ticket Routing
Compliance
Response
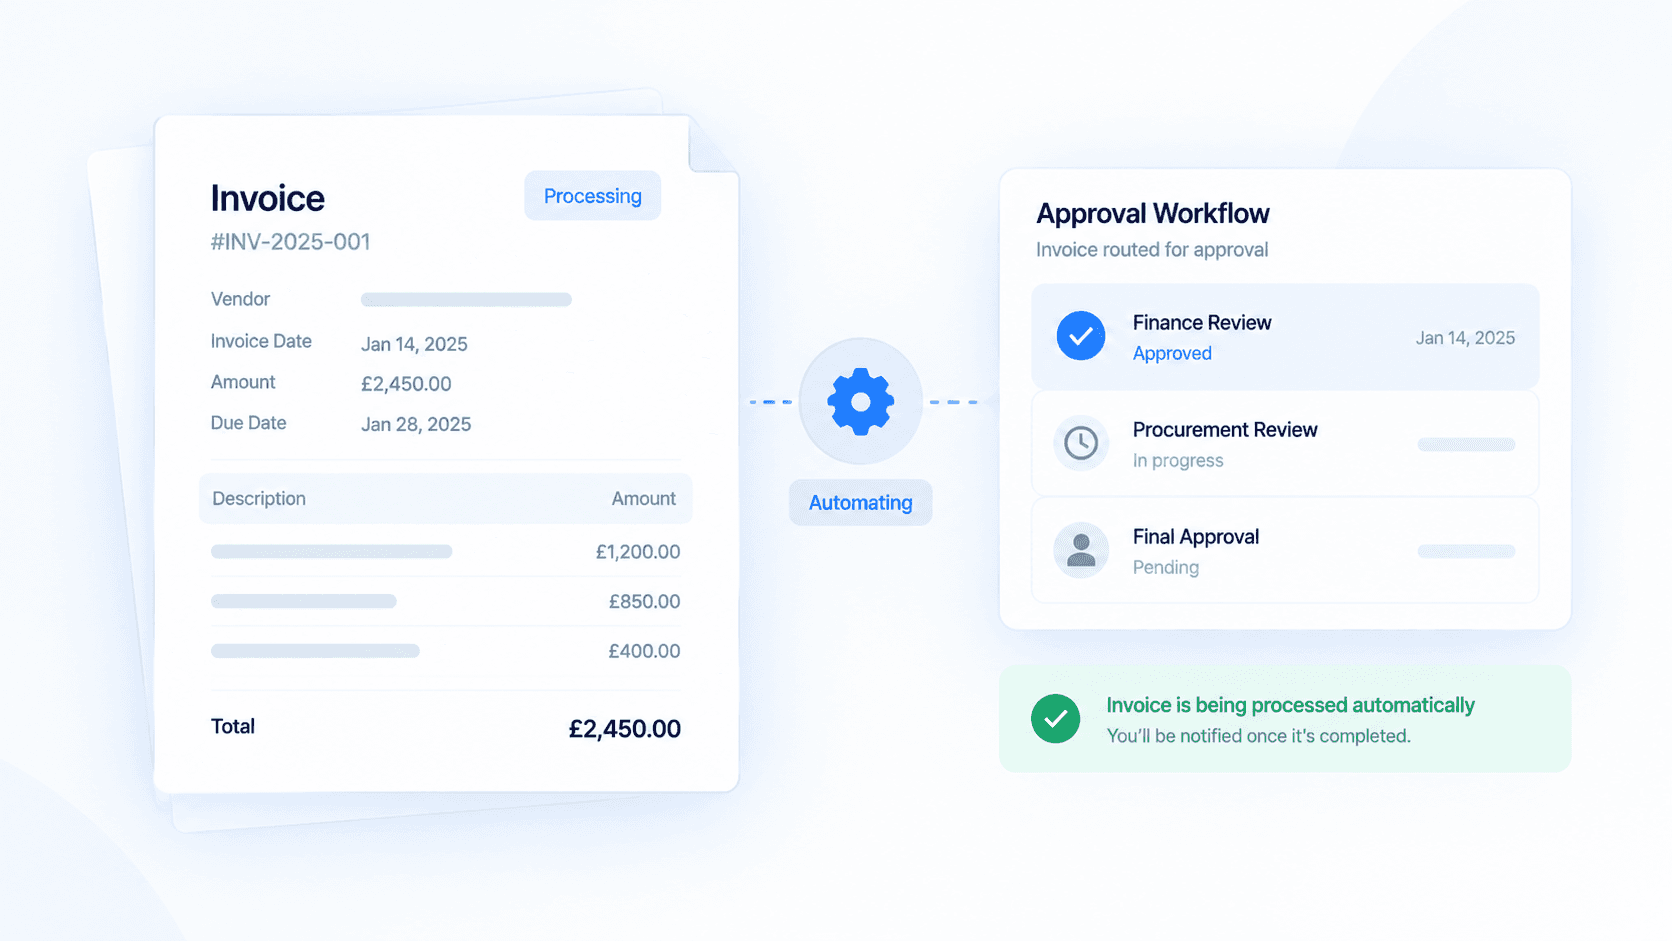
Automation
Two versions to cater every enterprise
Intelligent Platform powered by AI
100+ Super Intelligent Agents
|
ToggleNow SecOps for SAP GRC SAP GRC continues to support governance, risk and compliance processes. ToggleNow SecOps for SAP GRC extends the operating model connecting governance to continuous security operations, monitoring, automation and response. |
ToggleNow SecOps (with Embedded GRC) ToggleNow SecOps with embedded GRC adds the governance, risk and compliance layer. Specially designed for customers who doesn't have any GRC solutions. | |
|---|---|---|
| Risk Analysis & Materialization |
Uses SAP GRC ARA
|
Built-in analysis engine
|
| Access Request Management |
Uses SAP GRC ARM
|
Uses Digybots – Super Intelligent Agents
|
| Critical ID Assignment & Management |
Uses SAP GRC EAM
|
Uses Config ID management engine powered by Digybots
|
| Periodic Reviews + Access Certification |
Uses SAP GRC UAR/SOD Reviews
|
ReviewNow module
|
| Role Management |
Uses SAP GRC BRM
|
Standard capability since this requires CD pipeline
|
| Audit Reporting |
Standard reporting capabilities
|
Embedded GRC & ITGC reporting cards
|
| UI Data Masking |
Standard solution
|
Enhanced with auto scanning capabilities
|
A single operating model. Four ongoing capabilities.
A single operating model.
Four ongoing capabilities.
ToggleNow SecOps unifies access governance, compliance, security operations, and AI-driven automation into one continuous practice each capability reinforcing the others.
01
Access Governance
Establishes processes, enables self-service options to reduce your incident count.
02
Continued Compliance
Move compliance from a mere audit requirement to a continued compliance framework with well-defined workflow framework.
03
Security Operations
Keep an eye on what’s happening in your SAP system with built-in ITGC reporting capabilities. Enhance it to fit in your audit needs.
04
AI & Automation
Embed AI and automate repetitive activities while keeping humans accountable for key decisions.
Digybots – Intelligent Agent Group that automates mundane tasks
Digybots – Intelligent Agent Group that
automates
mundane tasks
Not just automation. We call it intelligent automation embedded with processes and industry & SAP recommended best practices.
Built for teams that value time and results.
People
SAP Security and GRC experts that understand the business context behind access, authorization and compliance decisions.
Process
Repeatable security operations replacing ad hoc tickets, spreadsheets and audit period firefighting.
Platform
SAP security technology embedded in access governance, GRC, monitoring, analytics and security controls.
AI
Intelligent execution automates repetitive operations, finds patterns and surfaces decisions that require human attention.
Can Do vs Did Do
The classic SAP security question is “Can this user do that?” SecOps asks, “They can, but did they?”
Authorization is what a user, role or technical identity can perform. Activity tells you what really happened. Bringing these views together provides better risk context and helps security teams prioritize the access and activity that matter.
CAN DO
Transaction: FB02, SE16N, F-53
Status: Assigned
Privileged Access: FF_FIN01
Status: Assigned/Active
Conflict: FB02 vs F-53
Status: Risk ID S026 active
Mitigation: FI_MC001
Status: Active for Risk ID S026
Change Logs: Enabled
DID DO
Transaction: FB02, SE16
Status: Executed
Privileged Access: FF_FIN01
Status: Never Executed in last 30 days
Conflict: FB02 vs F-53
Status: Risk ID S026 never exploited
Mitigation: FI_MC001
Status: Side A tcode executed. Side B wasn't
Change Logs:
User ABC changed the payment terms of a posted vendor invoice (Inv # 244) from Net 30 to Net 60 using FB02.
Can they do it — and did they?
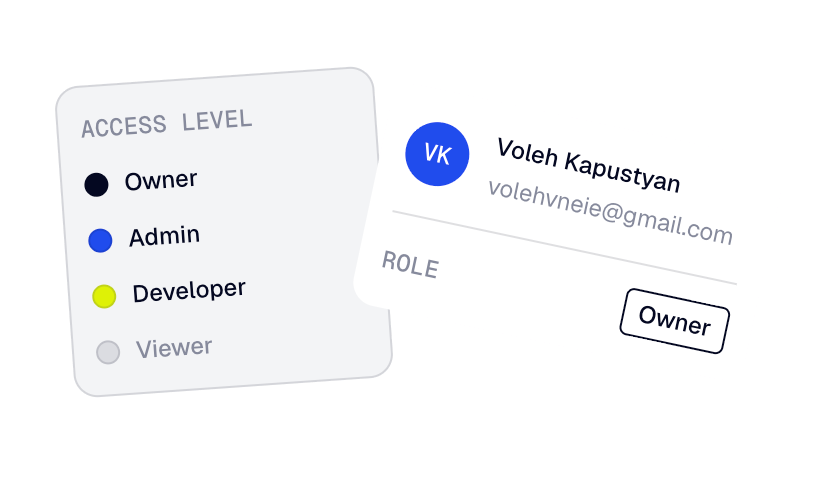
Authorization
Activity
What did this identity actually do? Which transactions were executed, what data was accessed, and when captured through logs, audit trails, and monitoring.
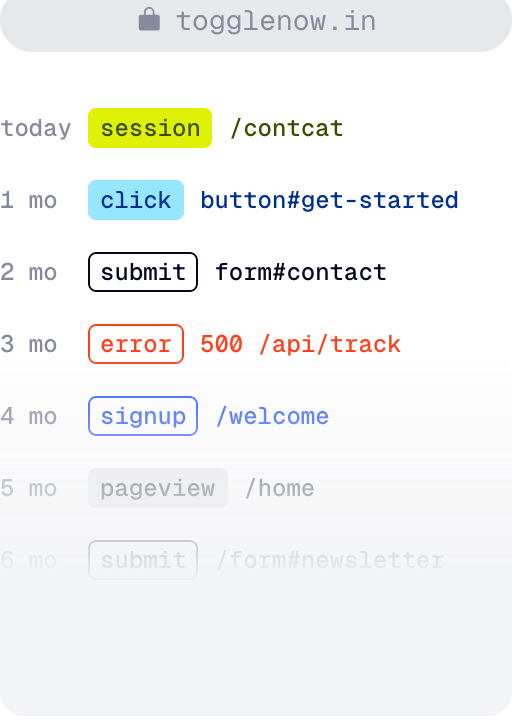
Activity
What did this identity actually do? Which transactions were executed, what data was accessed, and when captured through logs, audit trails, and monitoring.
Better Risk Context
Better Risk Context
SecOps across your
entire SAP landscape
SAP Environment
Coverage
ToggleNow SecOps for your
SAP environment
 SAP ECC
SAP S/4 HANA
SAP Fiori
SAP HANA
SAP GRC
SAP RISE
SAP Cloud
A complete operations
dashboard for SAP security
A complete operations dashboard for SAP security
Six operational groups working together as one continuous practice covering access, risk, monitoring, compliance, response, and automation across your SAP landscape.
Access Governance
Control who has access, why they have it, and whether that access is still appropriate
Risk Management
Identify and prioritize security risks across users, roles and authorizations.
Licensing Management
See what is actually happening across your SAP environment.
Compilance
Keep security controls active and evidence-ready every day.
Monitoring
Turn security signals into investigation and remediation.
Automation
Automate repetitive security operations while keeping people accountable for important decisions.
A single operating model. Four ongoing capabilities.
A single operating model.
Four ongoing capabilities.
ToggleNow SecOps unifies access governance, compliance, security operations, and AI-driven automation into one continuous practice each capability reinforcing the others.
Access Governance
ToggleNow SecOps for SAP GRC | ToggleNow SecOps GRC Platform
Cybersecurity
Audit Trail Enforcer | ThreatOps Suite
Artificial Super Intelligence
Digybots | FF Trust
Deploy. Operate. Transform.
Deploy. Operate. Transform.
What organizations need isn’t always another tool. They need an operating model that works in the real world.
Deploy
Configure the operating model, technology, controls and integrations.
Operate
Embedded SAP security and GRC expertise to lead SAP Security day-to-day operations.
Transform
Leverage the SAP landscape and continue to automate, optimize and improve the operating model.
Frequently asked
questions
Key questions about ToggleNow SecOps for SAP what it is, how it works, and how it fits into your security and GRC landscape.
What is ToggleNow SecOps for SAP?
ToggleNow SecOps for SAP is a continuous operating model for securing, monitoring, governing and improving a SAP environment. It combines SAP Security, access governance, GRC, security monitoring, compliance, automation and incident response into a single operational framework.
What’s the difference between ToggleNow SecOps for SAP and SAP GRC?
SAP GRC specializes in governance, risk, and compliance processes such as access risk analysis, access reviews, and controls. This is taken to the next level in continuous security operations by ToggleNow SecOps for SAP, connecting governance with monitoring, detection, automation, investigation and response.
Why organizations need ToggleNow SecOps for SAP?
Modern SAP landscapes are evolving all the time. Users, roles, applications, APIs, integrations, technical identities and cloud services can introduce new risk between periodic reviews. ToggleNow SecOps for SAP helps organizations continuously discover, prioritize and remediate security and compliance risks.
What does ToggleNow SecOps for SAP monitor?
Depending on the landscape and operating model, ToggleNow SecOps for SAP can monitor access changes, privileged user activity, technical/non-dialog user activity, authorization risks, critical and suspicious transactions, DB activity, security events, control status and other indicators of security risk.
Is ToggleNow SecOps for SAP replacing SAP GRC?
No, SAP GRC can be an important part of the security and governance ecosystem. ToggleNow SecOps for SAP connects GRC capabilities to broader security operations, monitoring, automation and response for a more continuous operating model.
What does the “Can Do vs. Did Do” idea mean?
“Can Do” represents what an identity is permitted to do. “Did Do” is what that identity actually did. Comparing authorization to activity adds additional context to prioritize real security risk.
Can ToggleNow SecOps for SAP automate SAP security and GRC tasks?
Yes. All repetitive activities such as risk analysis, access reviews, audit reporting, validation, executing workflows and preparing evidence can be automated. AI agents can help on some tasks but humans still need to oversee important security decisions.
Does ToggleNow SecOps for SAP work with S/4HANA and cloud SAP environments?
Yes. The operating model is applicable for environments such as SAP S/4HANA, Fiori, SAP BTP, SAP GRC, SAP HANA, RISE with SAP and other SAP cloud environments. Specific controls and integrations will vary depending on the landscape.
The Role of AI in ToggleNow SecOps for SAP?
Artificial intelligence can help security teams analyze large volumes of security information, prioritize risks, automate repetitive work, detect trends, and help with investigation and remediation workflows. ToggleNow requires human supervision in the event of major decisions.
How does ToggleNow execute SecOps?
ToggleNow brings together expertise in SAP Security and GRC, operating processes, technology and AI assisted automation. Based on the level of engagement, organizations can use a Deploy, Operate and Transform model to establish, operate and continuously improve their SAP security operations.
What results can ToggleNow SecOps for SAP provide?
The results are different depending on the initial environment and scope, but could include less manual effort, faster access reviews, better risk visibility, improved audit evidence, faster detection and response, and greater consistency in security operations. Quantified results should be benchmarked against the appropriate customer case study.
How do you measure ToggleNow SecOps for SAP Maturity in an organization?
A maturity assessment can determine if security operations are reactive, periodic, automated, continuous, or intelligent. The assessment should include people, processes, technology, monitoring, automation, governance and response capabilities.
Ready for the Shift from Reactive SAP Security to Continuous Control?
Ready for the Shift from Reactive SAP Security
to Continuous Control?
See how your SAP security operating model stacks up today and what it would take to move to continuous, intelligent security operations.